Trust Center
Security & privacy by Swiss design
Protect your organisation’s knowledge and operations on a platform built for critical infrastructure. No black boxes. No CLOUD Act. No compromises.
Our commitment to you
In our information age, knowledge is a critical asset. Organisations operating in demanding environments — banking, public administration, healthcare, critical infrastructure — cannot afford to compromise on trust. Six commitments define how we build and operate Phonemos:
Security
Enterprise-grade encryption, granular access control, and ISO 27001:2022 certification without exceptions.
Sovereignty
100% Swiss-owned and operated. US CLOUD Act not applicable. Data stays where you put it.
Privacy
GDPR-compliant data processing. Privacy by default in the product architecture. Responsible AI.
Compliance
ISO 27001, ISO 9001, ISO 14001. FINMA RS 4/2018. Auditable, documented, externally verified.
Resilience
High availability on Kubernetes, automated failover, 12-hour backups in a geographically separate data centre.
Transparency
Public status page, clear sub-processor disclosure, direct access to engineers and privacy experts.
The risk of extraterritorial laws
Many global software vendors are headquartered in jurisdictions with laws that allow their governments to compel data disclosure anywhere in the world — frequently under gag orders that prevent the customer from ever being notified. Among them: the US CLOUD Act, the UK Investigatory Powers Act, and the Australian Assistance and Access Act.
When you use a provider subject to these laws, your data residency in Europe becomes a paper shield — easily bypassed by a subpoena issued thousands of miles away.
The Swiss advantage: legal and political neutrality
Phonemos is 100% Swiss-owned, developed, and operated. This is not a point of pride — it is a structural legal advantage:
No compelled backdoor access. Swiss law does not allow the arbitrary, secret data extractions seen in other jurisdictions.
The Blocking Statute (Art. 271 StGB). Article 271 of the Swiss Criminal Code makes it a crime for foreign states to perform official acts — such as data seizures — on Swiss soil without following formal international legal assistance channels.
International Mutual Legal Assistance (IMAC). Any foreign request for data must be reviewed and validated by Swiss authorities. You are notified and your rights are protected under Swiss law before any data is discussed.
Full data localisation — cloud, any region, or on-premise
By default, all data is stored and processed in Switzerland. For organisations with specific regional requirements, Phonemos can be deployed on any AWS region. And for organisations operating in times of geopolitical turbulence who prefer to keep data entirely under their own control, a comprehensive on-premise option is available — and unlike many vendors who are phasing out self-hosted options, this is here to stay with Phonemos.
No vendor lock-in
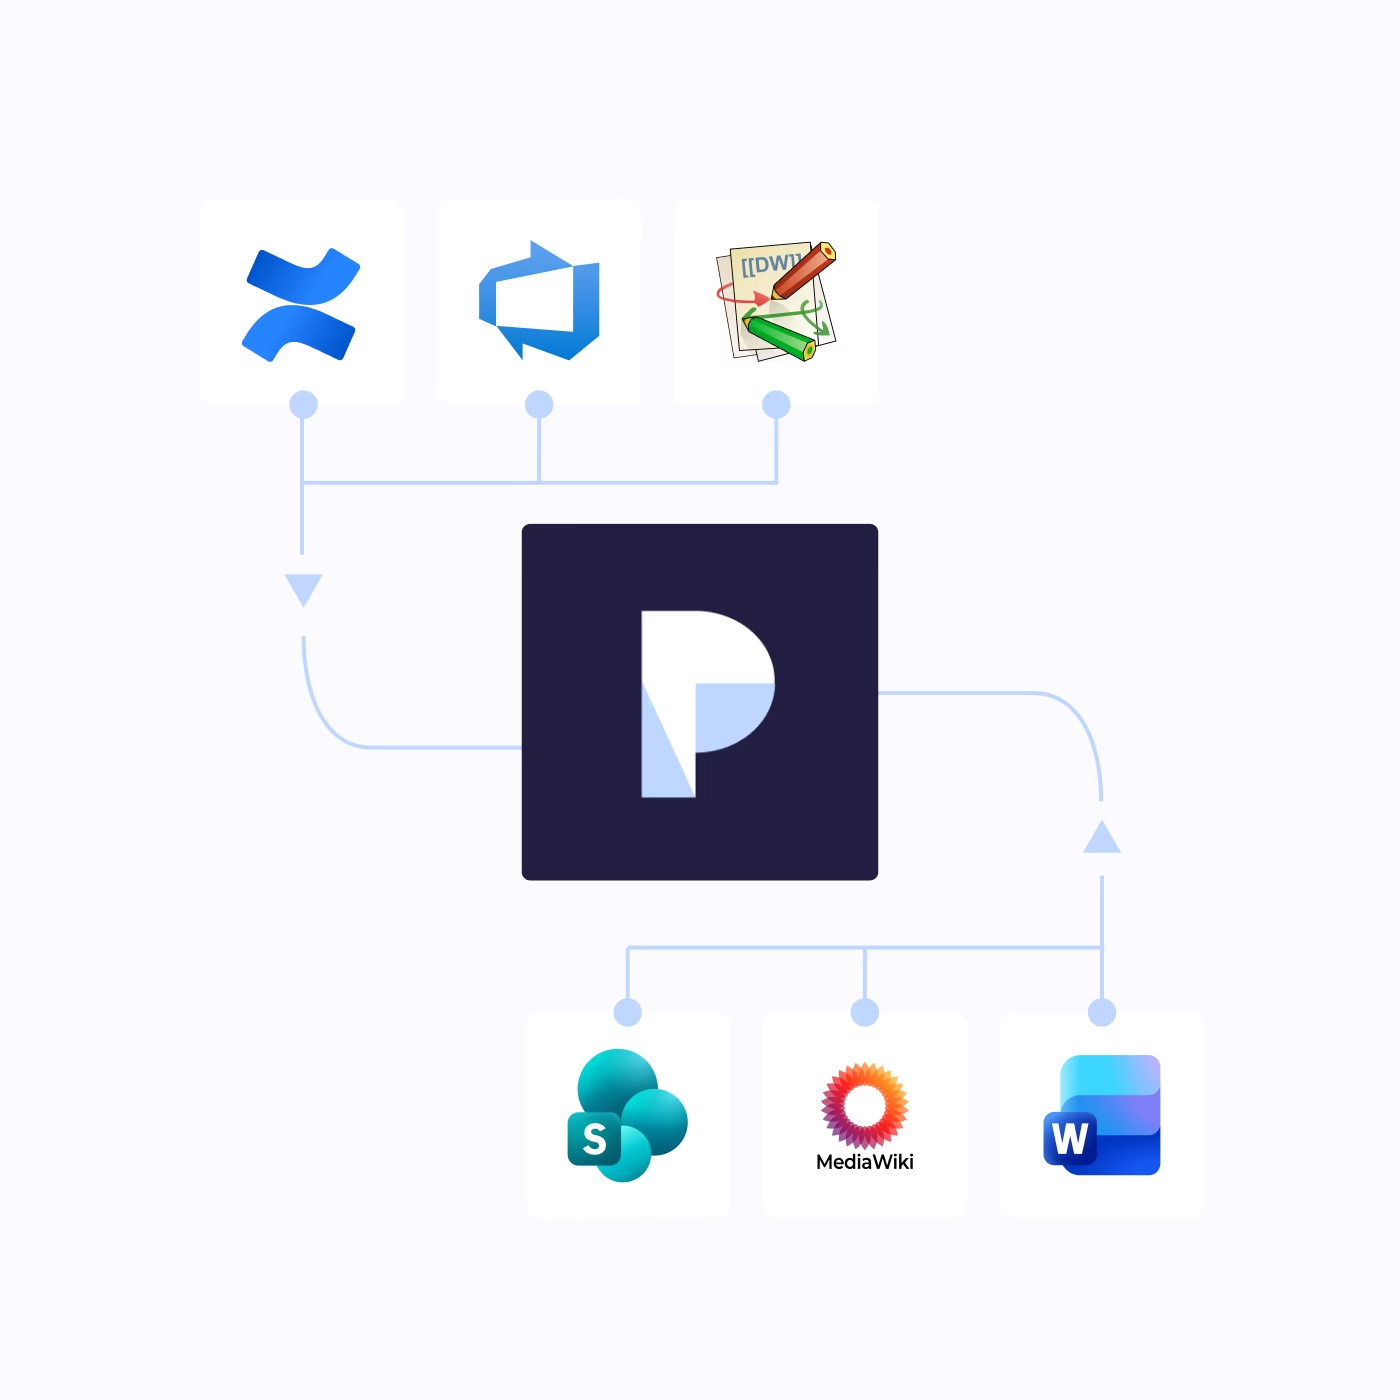
True professionalism is demonstrated by how a vendor handles the end of a lifecycle. We make exporting your data as easy as possible: PDF, Word, Markdown, HTML, ODF, LaTeX, and JSON are all supported. Migration tooling works in both directions.
A word on open source
Enterprise code escrow and government source code disclosure
Phonemos is not open source. Our product operates in a highly competitive market with large, well-funded competitors and AI developments that require constant investment. Too often we have seen open source vendors become passive custom software developers — only moving when a customer pays directly, and maintaining a growing legacy code base they seem unable to modernise. We don’t say this can’t be done right. But finding a long-term sustainable open source business model in addition to all the other challenges we face felt like one challenge too many.
When you choose Phonemos, you are not working with a startup or an investor-backed company looking for a quick exit. We are one of the 500 largest IT companies in Switzerland, 100% management-owned, with a decade-long track record since our founding in 2016. But we understand that a strong history may not fully address hypothetical risk scenarios such as default or end of support for on-premise deployments. If continuity is a concern, we are willing to negotiate source code escrow agreements for enterprise customers and government source code disclosure agreements, effectively neutralising the closed-source risk for national security interests.
Security: safety is not a paid upgrade
Security by default
Unlike many vendors who require additional payment for security essentials, all Phonemos plans include SSO (for example against your Entra ID), enforcement of two-factor authentication, and user lifecycle management integration with your existing provisioning. Security is standard, not a premium feature.
Granular permissions
Manage user access per site and portal to control who can log in where. Define access to topics through role-based access management — topic managers, content authors, or viewers. Refine further with Zones (protected folders) and fully customisable roles with individual permissions. You can even restrict administrator access to sensitive topics, for example where board-level content lives.
Security built into the process
Our information security management system has been ISO/IEC 27001 certified since 2018. We implement ISO/IEC 27001:2022 without any exclusions in the statement of applicability — all optional controls in Annex A are implemented. System security is reviewed and penetration tests are conducted at regular intervals by external security specialists.
Secure infrastructure
Phonemos is developed and operated in professionally managed, ISO 27001-certified data centres. Each customer instance is deployed with dedicated services, databases, and storage — your data is never in a shared database with other customers. Every drive and every backup is encrypted with customer-specific encryption keys.
Privacy
EU GDPR compliance
We offer EU GDPR-compliant data processing agreements with current standard contractual clauses. In our standard offering, your data is located and processed in Switzerland. Swiss privacy law is recognised as adequate by the European Commission — you have no additional compliance tasks beyond those required for any other European provider.
Privacy by default
Personal data must be managed professionally. Phonemos has permission mechanisms that prevent users from identifying other users in the system unless explicitly authorised to do so. Without that permission, all screens and history logs show changes by “unknown user” — protecting individual privacy even from internal actors.
Responsible AI
AI processing of personal data requires specific privacy safeguards. Rather than hard-coding a single large language model into Phonemos, we build on standard interfaces and give you the choice to use the LLM you trust — or a fully on-premise model. Per-site opt-in means sensitive content never touches an LLM unless explicitly configured.
Privacy expertise
When working with us, you benefit from our depth of experience in data privacy projects involving highly sensitive personal data in the government sector. We are not only a software vendor — if you need security and privacy concepts that require sign-off by an internal or government data protection officer, our team has the expertise to support you.
Compliance
Certified information security management
We operate an ISO/IEC 27001:2022 certified information security management system since 2018, with all 100 optional technical controls of Annex A implemented without exception — as proven by our statement of applicability. Enterprise customers can perform their own penetration tests and audits against our infrastructure, and receive confidential access to external audit reports.
Certified quality management
We operate an ISO/IEC 9001:2015 certified quality management system. Customer requirements are identified, implemented, verified, and continuously monitored over time.
Certified environmental management
We operate an ISO/IEC 14001:2015 certified environmental management system to continuously reduce our ecological footprint.
Industry-specific regulations
We are committed to meeting industry-specific regulatory requirements. For example, we are compliant with FINMA RS 4/2018 of the Swiss Financial Market Supervisory Authority. Reach out to discuss your specific requirements.
Ethical business practices
Our quality management system includes commitments to fair business practices: anti-corruption policies, prohibition of child labour, and fair wages throughout our supply chain.
These are documented, reviewed annually, and subject to external audit.
Resilience
Always on
We operate Phonemos around the clock with minimal downtime. Support is available during Swiss business hours as standard, with 7×24×365 support available for Enterprise plan customers.
High availability and failover
Phonemos runs on modern Kubernetes clusters. Depending on the size and SLA of your deployment, we implement fully automatic failover mechanisms and, where required, a full high availability setup for both scalability and redundancy.
Reliable backups
Your system is backed up every 12 hours. An encrypted offsite backup is stored in an independently
operated second data centre, geographically separate from the primary.
Transparency
Partnership without the black box
Trust is earned through visibility. We operate with a glass-house policy, giving you the insights needed to verify our promises rather than take them on faith.
Public system status and incident reports
We maintain a real-time status page documenting system availability and performance. In the event of a service disruption, we publish detailed post-mortem reports (root cause analysis) explaining what happened and what permanent fix was implemented.
Clear sub-processor disclosure
We maintain a lean and transparent list of sub- processors. You will always know exactly who handles any part of your data infrastructure. We commit to notifying customers in advance of any changes, giving you the right to object based on your compliance requirements.
Open security documentation
We provide enterprise customers with access to our Statement of Applicability (SoA), executive summaries of our latest penetration test results, and detailed architecture diagrams.
Direct access to expertise
We don’t hide behind multi-tiered support bots. Transparency means a direct line to the
engineers and privacy experts who build and maintain your system. Whether it’s an audit
preparation, a technical deep dive, or a review meeting with your compliance officers — our
team is available.

Need a security and privacy concept for your data protection officer?
